Smart Campus Equipment Standards: Security and Interoperability Checklist
Smart campus equipment should not pass technical acceptance because it carries a cybersecurity certificate or lists familiar protocols. The decisive question is whether the exact device, firmware, management platform, and cloud dependencies can operate securely within the campus architecture—and remain supportable after installation.
There is no single universal set of smart campus equipment standards covering connected classrooms, building controls, cameras, access readers, and environmental sensors. A defensible specification combines applicable legal requirements, product-specific standards, security capabilities, and witnessed interoperability tests. Each requirement needs evidence tied to the supplied configuration, not merely to the manufacturer’s brand.
Separate compliance, certification, and functional compatibility
These three forms of assurance answer different questions. Regulatory compliance determines whether equipment can legally be supplied or deployed in a jurisdiction. Certification demonstrates conformity within a defined assessment scope. Interoperability testing establishes whether particular systems exchange information and perform required functions together.
A CE marking is not an independent cybersecurity certification. An ISO/IEC 27001 certificate concerns an information security management system within its stated scope; it does not establish that every connected product is secure. Likewise, an electrical safety report does not demonstrate secure authentication or compatibility with a campus identity service.
Request certificate numbers, issuing bodies, standards editions, covered model variants, and relevant firmware versions. Where a certification scheme maintains a public directory, verify the entry. Treat “designed to meet” and “tested internally against” as different claims from independently certified conformity.
Define the trust boundary before selecting devices
A room sensor reporting temperature presents a different risk from a door controller authorizing entry. Both may use the same network, but their consequences, availability requirements, and recovery procedures differ.
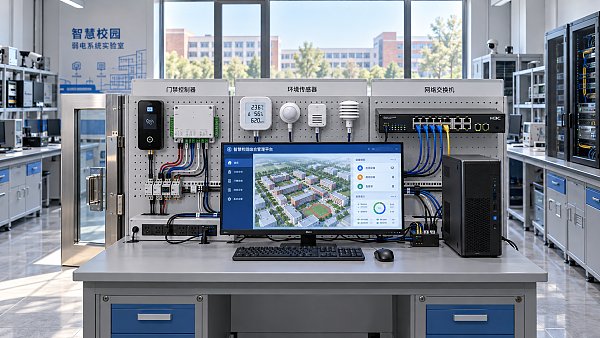
Document the complete service path: endpoint, gateway, local controller, management server, mobile application, supplier cloud, and third-party integrations. Identify where credentials reside, where commands originate, and which functions stop when a dependency becomes unavailable. A device with a local interface may still depend on cloud services for licensing, provisioning, or administrator authentication.
The resulting architecture should distinguish teaching networks, building systems, physical security, administrative services, and guest access. A VLAN alone is not a sufficient security boundary: firewall rules, identity controls, management access, and monitored exceptions determine what that separation achieves.
Security checks that require demonstrable evidence
Identity, authentication, and administrative access
- Eliminate shared default credentials. Require unique provisioning credentials or a controlled first-use enrollment process. Verify factory reset behavior and whether reset reintroduces an insecure state.
- Separate human and machine identities. Administrator accounts, integration accounts, and device certificates need independent permissions and revocation paths.
- Test campus network authentication. Where IEEE 802.1X is required, verify the supported EAP method, certificate enrollment, server certificate validation, renewal, and recovery after expiry. “802.1X supported” is insufficient detail.
- Protect privileged management. Require role-based access and multifactor authentication for management platforms where supported. Document compensating controls for constrained endpoints that cannot provide equivalent controls directly.
- Control supplier access. Remote maintenance should be explicitly enabled, time-limited where feasible, attributable to an individual, and logged. Undocumented persistent tunnels are unacceptable.
Test account revocation across the whole system. Disabling a campus directory account should not leave an independent cloud administrator session or local maintenance account available indefinitely. Identify emergency access arrangements and ensure their use is controlled and auditable.
Encryption and certificate management
Specify protected communication paths rather than accepting a general claim of “encrypted data.” Check endpoint-to-gateway, gateway-to-server, browser-to-platform, and platform-to-cloud connections separately. Require currently approved protocol configurations under campus policy, such as appropriately configured TLS 1.2 or TLS 1.3 where applicable.
Certificate handling is as important as encryption support. Verify trust-store management, hostname validation where applicable, replacement of factory certificates, renewal procedures, and private-key protection. A system that encrypts traffic but accepts any server certificate remains exposed to impersonation.
For stored data, establish which credentials, recordings, identifiers, and configuration secrets are retained. Assess encryption, key ownership, backup protection, and secure deletion according to their sensitivity. Encryption alone does not justify unrestricted collection of classroom or occupancy data.
Firmware integrity, updates, and vulnerability handling
Require authenticated firmware updates and documented protection against unauthorized software installation. Secure boot, where available and appropriate, adds protection during startup but does not replace runtime access controls or timely patching.
Ask suppliers to demonstrate interrupted-update recovery, configuration preservation, and controlled rollback. Rollback can aid recovery, but unrestricted installation of vulnerable older firmware can undermine security. The required behavior must reconcile service continuity with anti-rollback controls.
- Obtain a published vulnerability-reporting channel and a documented disclosure process.
- Request a software bill of materials in a usable format, such as SPDX or CycloneDX, with a defined update process.
- Require vulnerability assessments that distinguish affected components from exploitable product configurations.
- Define patch notification, remediation, and escalation commitments according to risk.
- Confirm whether security fixes require an active subscription, a gateway upgrade, or chargeable service visits.
An SBOM is an inventory input, not proof that a product is vulnerability-free. Its practical value depends on component identification, maintenance, and the supplier’s ability to explain product exposure when vulnerabilities emerge.
Match interoperability standards to the actual function
Protocol names establish only a starting point. Compatibility depends on profiles, optional services, data models, security modes, version support, and licensing. Require an interface matrix identifying exactly which functions can be read, written, subscribed to, exported, and administered.
Building controls and environmental monitoring
For BACnet equipment, request the Protocol Implementation Conformance Statement and check any BACnet Testing Laboratories listing against the proposed model. Verify required objects, services, writable properties, alarm handling, schedules, and trend access. A listed device may still lack an optional function essential to the project.
BACnet Secure Connect, standardized within BACnet, provides a TLS-based communication option. Its deployment also introduces certificate and hub-management requirements. Support for BACnet/IP does not establish support for BACnet/SC, and adding a secure segment does not automatically protect legacy traffic elsewhere.
For Modbus integrations, establish the register map, scaling, byte order, write permissions, and exception behavior. Conventional Modbus TCP should not be treated as providing authentication or confidentiality by itself. Where gateways or security-capable implementations are proposed, test the complete protected path.
Video and physical access
For cameras and video platforms, verify the relevant ONVIF profiles and the exact product’s conformance listing. Profile support must match the required use: video streaming, recording access, metadata, and events are not interchangeable capabilities. Test event interpretation and search workflows, not just whether a live image appears.
For reader-to-controller communication, OSDP under IEC 60839-11-5 supports capabilities beyond legacy Wiegand wiring, including a Secure Channel option. Require Secure Channel to be enabled and correctly provisioned where specified; an OSDP connection is not necessarily encrypted merely because the protocol supports it.
Door release, emergency egress, and fire-system interactions must follow applicable local requirements and the approved safety design. Network isolation or server failure must not create an unsafe access condition.
Classroom devices, APIs, and messaging
For classroom equipment, test the required control, content-sharing, and identity workflows against actual operating systems and campus network policies. Discovery mechanisms that work on a flat demonstration network may fail across routed segments unless explicitly supported and configured.
REST APIs and MQTT support do not provide semantic interoperability on their own. Require documented schemas, units, timestamps, identifiers, topic permissions, rate limits, versioning, and error behavior. Two systems can exchange valid messages while interpreting occupancy, alarm states, or room identities differently.
Run acceptance tests on the proposed configuration
Use production-equivalent firmware, licenses, controllers, and security settings. Record expected outcomes before testing, including acceptable recovery times and data-loss limits. Supplier demonstrations on unrestricted networks should not substitute for this environment.
Inspect logs during these tests. Security-relevant events should include authentication failures, privilege changes, configuration changes, firmware actions, and remote access. Verify time synchronization and export to the campus monitoring environment. Logs that exist only inside an inaccessible supplier portal provide limited independent visibility.
Make lifecycle support part of technical acceptance
Require a contractual security-support end date for the supplied equipment, not simply a warranty period. Clarify advance notice of end of support, access to firmware, replacement-controller compatibility, and the treatment of equipment already installed when a cloud service changes.
Exit capability also needs testing. Export configuration, room mappings, historical measurements, event records, and other required data in documented formats. Determine whether another platform can use those exports without proprietary conversion services. Where private keys or credentials should not be exported, define secure replacement and reenrollment procedures instead.
Assign each unresolved issue a disposition: acceptance blocker, time-bound remediation, or approved exception with compensating controls. A certificate can support that decision, but it cannot replace evidence that the delivered system meets the campus’s security boundaries, operating requirements, and support obligations.
Search News
Hot Articles
- Outdoor RidesTEA: Water Parks and Museums Outpace Theme Parks in 2025 Attendance GrowthOct 29, 2026
- Smart Campus TechSmart Campus Equipment Standards: Security and Interoperability ChecklistOct 29, 2026
- Musical InstrumentsMusic China 2026 Opens Tomorrow, With 800-Plus Events Connecting TradeOct 28, 2026
Popular Tags
Need ExpertConsultation?
Connect with our specialized leisureengineering team for procurementstrategies.
Recommended News
 Oct 29, 2026Smart Campus Equipment Standards: Security and Interoperability ChecklistExplore smart campus equipment standards with a practical security and interoperability checklist. Verify supplier claims, reduce integration risks, and make confident purchasing decisions.● Institutional Buyer
 Sep 28, 2026How U.S. Schools Can Choose Laboratory Equipment for Safe, Compliant Science LabsSchool laboratory equipment USA: learn how to select safe, compliant lab furniture, ventilation, emergency systems, and durable tools for K–12 science labs.● Institutional Buyer
 Sep 16, 2026How to Source Educational Furniture Worldwide for Safe, Flexible Learning SpacesEducational furniture worldwide: learn how to source safe, flexible, durable learning-space solutions while controlling compliance, logistics, and lifecycle costs.● Institutional Buyer
 Aug 31, 2026How to Plan Smart Classroom Solutions That Improve Learning and IT ManageabilitySmart classroom solutions: learn how to plan secure, scalable teaching spaces that improve learning, simplify IT management, and reduce lifecycle costs.● Institutional Buyer
 Aug 01, 2026How to Specify an EN54 School PA System for Safe, Compliant Campus Voice EvacuationEN54 school PA system specification guide for safer, compliant campus voice evacuation. Learn zoning, intelligibility, monitoring, tender tips, and handover checks.● Institutional Buyer
 Jul 15, 2026Vietnam Tightens Import Rules for Smart Campus TechVietnam Tightens Import Rules for Smart Campus Tech: learn how MOIT’s 2026 data hosting and NEP connection rules may reshape import approval, sourcing timelines, and delivery planning.● Institutional Buyer
 Jul 14, 2026Thailand TISI Tightens Rules for Smart Campus TerminalsThailand TISI tightens rules for smart campus terminals, requiring Thai speech recognition and local biometric data storage. Learn the compliance impact, timeline risks, and what exporters must do now.● Institutional Buyer
 Jul 13, 2026Red Sea Rerouting Lifts Smart Campus Tech Shipping CostsRed Sea rerouting lifts Smart Campus Tech shipping costs, extends Asia-Europe booking lead times, and delays delivery. See what exporters, buyers, and logistics teams should do now.● Institutional Buyer
 Jul 12, 2026Event Technology for Live Venues: What Systems Matter Most for Seamless Operations?Event technology defines how live venues handle ticketing, AV, access, and monitoring. Discover which systems matter most for seamless operations, higher uptime, and better guest experiences.● Institutional Buyer
 Jul 11, 2026What Is a Campus Procurement Platform and How Does It Improve School Purchasing Workflows?Campus procurement platform explained: learn how it streamlines school purchasing workflows, improves approval control, boosts spend visibility, and reduces delays across campus buying.● Institutional Buyer
 Jul 10, 2026Vietnam Raises Smart Campus Tech Import Tariff to 12%Vietnam Raises Smart Campus Tech Import Tariff to 12%: explore how the new Vietnam smart campus tech tariff impacts pricing, sourcing, and local assembly strategies across Southeast Asia.● Institutional Buyer
 Jul 10, 2026Interactive Document Camera vs Webcam: Which Works Better for Smart Classrooms?Interactive document camera vs webcam: discover which delivers clearer content sharing, faster lesson flow, and better hybrid teaching performance for smart classrooms.● Institutional Buyer
 Jul 09, 2026RCEP Rule Adds Carbon Footprint Filings for Smart Campus Tech ExportsRCEP Rule reshapes Smart Campus Tech exports: learn how new carbon footprint filings for Singapore, Thailand, and Vietnam affect customs clearance, lead times, and compliance planning before October 1, 2026.● Institutional Buyer
 Jul 09, 2026Basketball Hoops for Campuses: Which Backboard, Rim, and Mounting Type Fits Your Site?Basketball hoops for campuses: compare backboard, rim, and mounting options by site needs. Learn how to choose safer, longer-lasting systems for outdoor courts, gyms, and multipurpose halls.● Institutional Buyer
 Jul 09, 2026Modular Educational Furniture: What to Check Before Planning Flexible ClassroomsModular educational furniture: learn what to check before planning flexible classrooms, from safety and durability to teaching fit, supplier quality, and long-term value.● Institutional Buyer
 Jul 08, 2026Shenzhen-Yokohama Port Delays Fall to 2.1 DaysShenzhen-Yokohama Port Delays fall to 2.1 days, cutting shipment cycles by 5–7 days for smart campus equipment. See how faster port efficiency can ease Q3 school delivery pressure.● Institutional Buyer
 Jul 07, 2026FBX Slide Pushes Smart Campus Freight Below $980/FEUFBX Slide Pushes Smart Campus Freight Below $980/FEU as Asia-Europe rates tumble. Discover what this means for smart campus shipments, booking risks, and cost-saving opportunities.● Institutional Buyer
 Jul 07, 2026Math Manipulatives Bulk Price Guide: Cost Drivers, Pack Sizes, and School Budget PlanningMath manipulatives bulk price explained: compare cost drivers, pack sizes, landed costs, and school budget planning tips to source smarter and avoid hidden expenses.● Institutional Buyer
 Jul 04, 2026RCEP Update Expands Indonesia Duty-Free Quota for Edu DevicesRCEP Update Expands Indonesia Duty-Free Quota for Edu Devices: learn how the new 80,000-unit quota reshapes export costs, compliance, and school procurement opportunities in Indonesia.● Institutional Buyer
 Jul 03, 2026Indonesia Enforces ID-SNI Labels on Smart Campus ImportsIndonesia Enforces ID-SNI Labels on Smart Campus Imports: learn how the new rule affects labeling, customs clearance, certification, and delivery readiness for compliant market entry.● Institutional Buyer
 Jul 03, 2026How to Choose Indoor School Sports Equipment for Age Groups, Space, and Safety NeedsIndoor school sports equipment buying guide for schools: learn how to match age groups, space limits, and safety standards to choose durable, efficient solutions.● Institutional Buyer
 Jul 02, 2026Chromebook Charging Stations for Schools: Cart vs Cabinet vs Wall-Mount OptionsChromebook charging stations for schools compared: cart, cabinet, and wall-mount options. Discover the best fit for security, space, mobility, and budget before you buy.● Institutional Buyer
 Jul 01, 2026Indonesia Opens RCEP Fast Track for Smart Campus IoTIndonesia opens an RCEP fast track for Smart Campus IoT, cutting Jakarta customs clearance to 12 hours for eligible HS 8517.62 devices. See who qualifies and how to prepare.● Institutional Buyer
 Jun 30, 2026Flexible Learning Spaces for K-12 and Higher Ed: Layout Ideas, Furniture, and Tech NeedsFlexible learning spaces for K-12 and higher ed: explore practical layout ideas, durable furniture, and smart tech strategies that improve teaching, flexibility, and long-term campus value.● Institutional Buyer